Firefox displays a warning whenever it detects an SSL certificate issue or an HTTP connection on a site that should be using HTTPS. This blocking protects the data exchanged between the browser and the server. Accessing an unsecured site on Firefox is still possible in some cases, but the approach varies depending on the type of warning displayed.
Expired Certificate, HSTS, and HTTP: Three Firefox Blocks to Distinguish
Not all alert messages from Firefox are the same. Before trying to bypass a warning, identifying the nature of the block helps avoid wasting time on unnecessary actions, or worse, exposing oneself to a real risk.
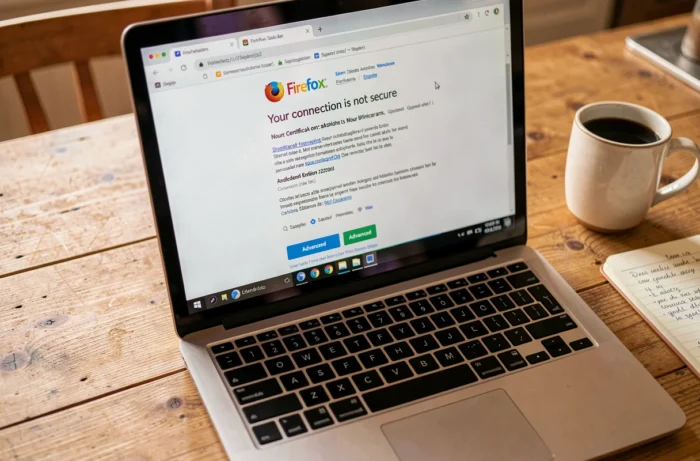
An expired or self-signed certificate triggers the page “Warning: Potential Security Risk.” Firefox then offers an “Advanced” button that allows adding an exception. This is the most common case on internal networks, box interfaces, or outdated sites that are no longer maintained.
A site that implements HSTS (HTTP Strict Transport Security) requires Firefox to connect via HTTPS with no possibility of exemption. The browser simply refuses to display the page. Trying to “proceed anyway” does not work here: you need to check the entered address, the device’s clock, or contact the site administrator.
Finally, a site using simple HTTP (without any certificate) displays a crossed-out padlock in the address bar. Firefox does not block access by default but indicates that the connection is not encrypted. The detailed procedure for unsecured sites on Firefox covers each of these scenarios with the appropriate actions.
Adding a Certificate Exception in Firefox: Step-by-Step
When the warning concerns an invalid certificate (and not an HSTS block), Firefox allows the addition of a manual exception. The process takes a few seconds.
- On the warning page, click the “Advanced” button located at the bottom of the alert message
- Read the details of the displayed error (expired certificate, mismatched domain name, unrecognized authority)
- Click “Accept the Risk and Continue” to save a temporary exception in the browser
This exception remains active for the concerned site. Firefox will not ask for confirmation during subsequent visits unless the certificate changes again.
Removing a Saved Exception
To revert, open Firefox settings, then the “Privacy & Security” section. In the “Certificates” part, the “View Certificates” button provides access to the “Servers” tab where all manually added exceptions are listed. Select the site and click “Remove” to restore the default behavior.
Advanced Firefox Settings: about:config and HTTPS Only Mode
Firefox has included a “HTTPS Only” mode in several versions that automatically forces encrypted connections. This mode, enabled by default in recent versions, can cause blocks on sites that simply do not offer HTTPS.
To temporarily disable it: open Firefox settings, scroll down to “Privacy & Security,” then look for the “HTTPS Only Mode” section. Three options appear: enable the mode on all windows, only in private browsing, or disable it completely.
Modifying a Setting in about:config
The about:config page provides access to the browser’s internal settings. Type about:config in the address bar, accept the warning, then search for the relevant setting. For HTTPS mode, the relevant key is dom.security.https_only_mode: setting it to “false” disables automatic redirection to HTTPS.
Modifying about:config is not trivial. Each changed setting remains active until manually restored. Noting the original values before any modification allows for easy reversal.
Real Risks of an Unsecured Site and Precautions to Take
Bypassing a security warning is not a neutral act. A padlock does not prove that a site is trustworthy: phishing sites also use valid HTTPS certificates. Conversely, an old HTTP site without a certificate can be perfectly legitimate, but the connection remains readable by anyone intercepting the network traffic.
On a public Wi-Fi, the risk increases significantly. HTTPS protects the content of exchanges, but a fake access point may attempt to capture credentials via a fraudulent login page. For sensitive operations (banking, messaging), mobile data is preferable to public Wi-Fi. A VPN is an alternative if mobile network is not available.
- Never enter a password or banking details on an HTTP site, even after adding an exception
- Always check the domain name in the address bar before entering any credentials
- Prefer 4G/5G for sensitive connections when an unknown Wi-Fi network is the only option
- Re-enable HTTPS only mode as soon as the consultation of the unsecured site is finished
DNS-over-HTTPS and VPN: What They Really Protect on Firefox
Firefox natively offers DNS-over-HTTPS (DoH), which can be activated in the browser’s network settings. This protocol encrypts DNS queries, preventing a third party on the network from seeing which sites are being visited. However, it does not make an HTTP site safe and does not encrypt the content of the visited pages.
A VPN, on the other hand, encrypts all traffic between the device and the VPN server. Combined with DNS-over-HTTPS, it significantly reduces exposure on an untrusted network. But neither of these tools replaces a valid SSL certificate on the server side: they protect the communication channel, not the reliability of the site itself.
Accessing an unsecured site on Firefox therefore requires understanding what each layer of protection actually covers. Disabling a warning to consult a local router interface is nothing compared to entering personal data on an unknown HTTP site. The browser provides the tools to manage both cases, provided that protections are restored as soon as the occasional consultation is finished.